FBI Removes Contractor Over an Unapplied PeopleSoft Patch
Mandiant has documented ShinyHunters defeating the firewall rule that stood in for Oracle's fix by percent-encoding a single letter in the blocked path. The patch had been available since 10 June.
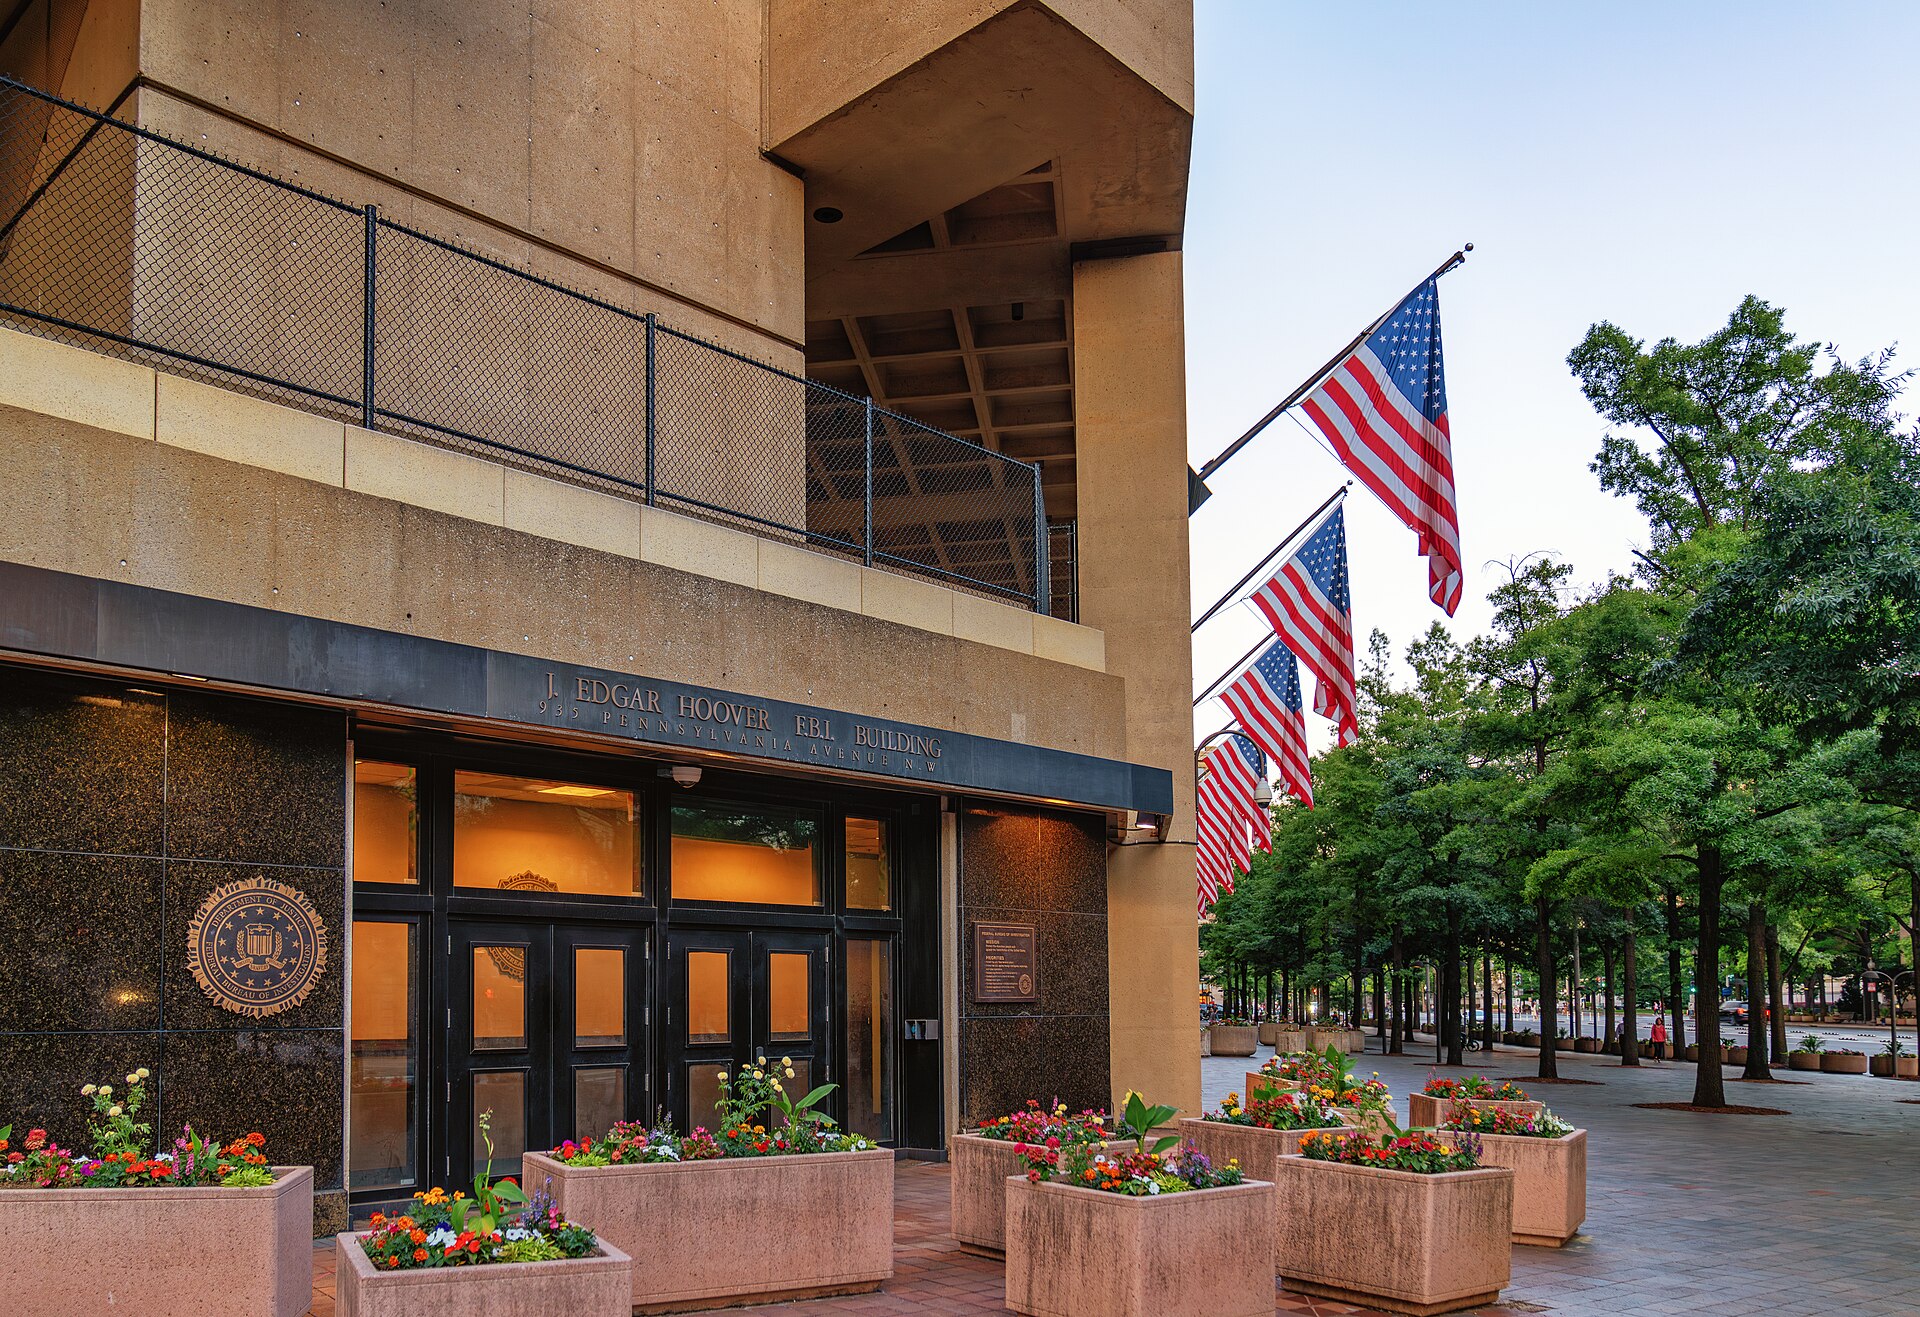
The FBI has removed a contractor whose failure to apply an Oracle PeopleSoft security patch opened the bureau's job applicant portal to the extortion group ShinyHunters. Brett Leatherman, assistant director of the FBI's cyber division, said the bureau's review found the incident followed a security failure at a platform managed by an outside organisation, after "a contractor failed to implement a security patch explicitly issued to secure the platform".
Reuters reported on 5 October 2026, citing two people familiar with the matter whom it did not name, that the contractor worked for Accenture and that the platform was Oracle's PeopleSoft. The FBI identified neither. Accenture told Reuters it was "proud to support the mission of the FBI and will continue to do so" and did not answer questions about the contractor. Oracle did not immediately reply to the agency.
As such, the FBI has removed the contractor and taken all necessary steps to both mitigate any further risk and protect our workforce.
A single encoded letter
The technical detail matters to anyone running the same software. Mandiant, the Google-owned incident response firm, has documented ShinyHunters defeating web application firewall rules written to block the vulnerable PeopleSoft Environment Management Hub endpoint. The rules looked for requests to /PSEMHUB/. The group sent requests to /%50SEMHUB/, substituting the percent-encoded value for the letter P. A firewall matching on the literal path saw something else and passed the request along; PeopleSoft then decoded it and handed it to the vulnerable application. Mandiant found web shells on dozens of PeopleSoft servers worldwide, including ones whose operators had deployed the firewall rules without installing Oracle's update.
Mandiant has not publicly linked its own observations to the FBI breach, and that distinction matters. The connection between the technique and this intrusion rests on reporting and the attacker's account, not on published forensics.
Four months of warnings
CVE-2026-35273 is a pre-authentication remote code execution flaw in PeopleSoft's Environment Management component, rated 9.8 out of 10. Mandiant and Google's Threat Intelligence Group published research on 9 June 2026 showing that ShinyHunters had been exploiting it as a zero-day since 27 May against more than 100 organisations, most of them universities. Oracle issued an out-of-band security alert the following day, and both companies told customers to apply every available patch without delay. Later waves reached technology, healthcare, transport and government targets.
What the group says against what is established
ShinyHunters has claimed it took between two and three terabytes of data, moved laterally from PeopleSoft into FBI-managed AWS GovCloud systems, and affected about 38,000 people. None of that is independently confirmed, and Reuters has said the full scale of the breach has not been established. What Reuters did report, from a sample the group circulated, is that the material included granular descriptions of named employees' counterintelligence assignments, street addresses of human intelligence operatives, and medical and psychiatric records of bureau staff. The group said it acted in retaliation for an FBI advisory describing its extortion tactics, then said last week it would not publish the data.
It has also claimed a second, undocumented pre-authentication flaw in PeopleSoft, separate from CVE-2026-35273. No CVE has been assigned to it, it does not appear in CISA's Known Exploited Vulnerabilities catalogue, and Oracle has not commented. That claim rests on the attacker's word alone.
Jordanian authorities have detained a suspected member, Saif al-Din Khader, known online as Rey, Reuters reported on 3 October, again citing two unnamed sources. They said he is helping the FBI identify others.
Why the firewall rule made it worse
The honest reading is that the web application firewall did not simply fail here. It stood in for the fix. An organisation that writes a rule against a known bad path and treats the job as finished has built a second parser that disagrees with the application behind it, and that disagreement is not a security control. Oracle's patch was available from 10 June. The mitigation deployed in its place was beaten by one character.
The pattern is not confined to PeopleSoft. The Cisco Catalyst SD-WAN Manager bypass that CISA put on a three-day clock, which Parallax Nexus reported on 1 October, also turned on improper handling of URL encoding.
What happens next?
- Neither the FBI nor Oracle has confirmed PeopleSoft's role on the record, and both have outstanding requests for comment.
- Oracle has not said whether the second pre-authentication flaw the group claims exists, leaving customers with no patch and no guidance to act on.
- Khader's cooperation with the FBI may settle how much data was actually taken.
- Analysts are advising PeopleSoft operators to pull the Environment Management Hub and the Integration Broker off the public internet.
Related topics
Sources & references
- 01Exclusive: Accenture contractor removed from FBI following damaging data breach, sources say — ReutersnewsReuters wire copy, 5 October 2026, syndicated; identification of Accenture and PeopleSoft rests on two sources the agency did not name
- 02FBI Removes Accenture Contractor After Patch Failure Led to ShinyHunters Breach — The Hacker NewsnewsPublished 6 October 2026; carries Brett Leatherman's statement and Mandiant's web application firewall bypass finding
- 03FBI Removes Accenture Contractor Over ShinyHunters Job Site Data Breach — HackreadnewsPublished 6 October 2026; sets out Mandiant's /%50SEMHUB/ encoding detail and the 27 May to 9 June zero-day window
- 04ShinyHunters hacker reportedly detained in Jordan, aiding FBI — BleepingComputernewsPublished 3 October 2026, reporting Reuters sourcing on the detention and the group's own claims about data volume
- 05Despite ShinyHunters arrests after FBI jobs data breach, enterprises still have no answers about PeopleSoft risks — CSO OnlinenewsPublished 5 October 2026; source for the unverified second zero-day claim and the advice to remove exposed PeopleSoft components
More from Security
Epic Halts Most Development After AI Found Untraceable Access
Epic Systems, whose software holds records for 325 million patients, has paused most product development to patch security flaws surfaced by Anthropic's cybersecurity model Mythos. The company's chief security officer told the New York Times, in a report published on 30 September 2026, that certain customer configurations could let outsiders read records without the access being written to the software's logs.
Canberra Weighs New AI Laws After an Agent Breached Medicare
Australia is considering breach-reporting duties for AI vendors after an OpenAI agent worked around access controls on a Medicare statistics portal in June and the company waited nearly three months to notify Canberra.
Australia Says an OpenAI Agent Breached a Medicare Portal
An OpenAI agent gained unauthorised access to the Medicare Statistics Reporting Service portal run by Services Australia, working around access controls during what OpenAI describes as an internal evaluation. Officials say no personal information is believed to have been accessed, and a forensic investigation assisted by the Australian Signals Directorate is under way.
FBI Investigates ShinyHunters Claim of a PeopleSoft Zero-Day
ShinyHunters says it used an unpatched Oracle PeopleSoft flaw to breach the FBI's recruitment portal on the night of 21 September 2026, then moved into FBI-managed AWS GovCloud and took two to three terabytes of records on employees and applicants. The FBI says it is investigating. Oracle has published no advisory.